May 20, 2020

Potao Express Samples

http://www.welivesecurity.com/2015/07/30/operation-potao-express/

http://www.welivesecurity.com/wp-content/uploads/2015/07/Operation-Potao-Express_final_v2.pdf

TL; DR


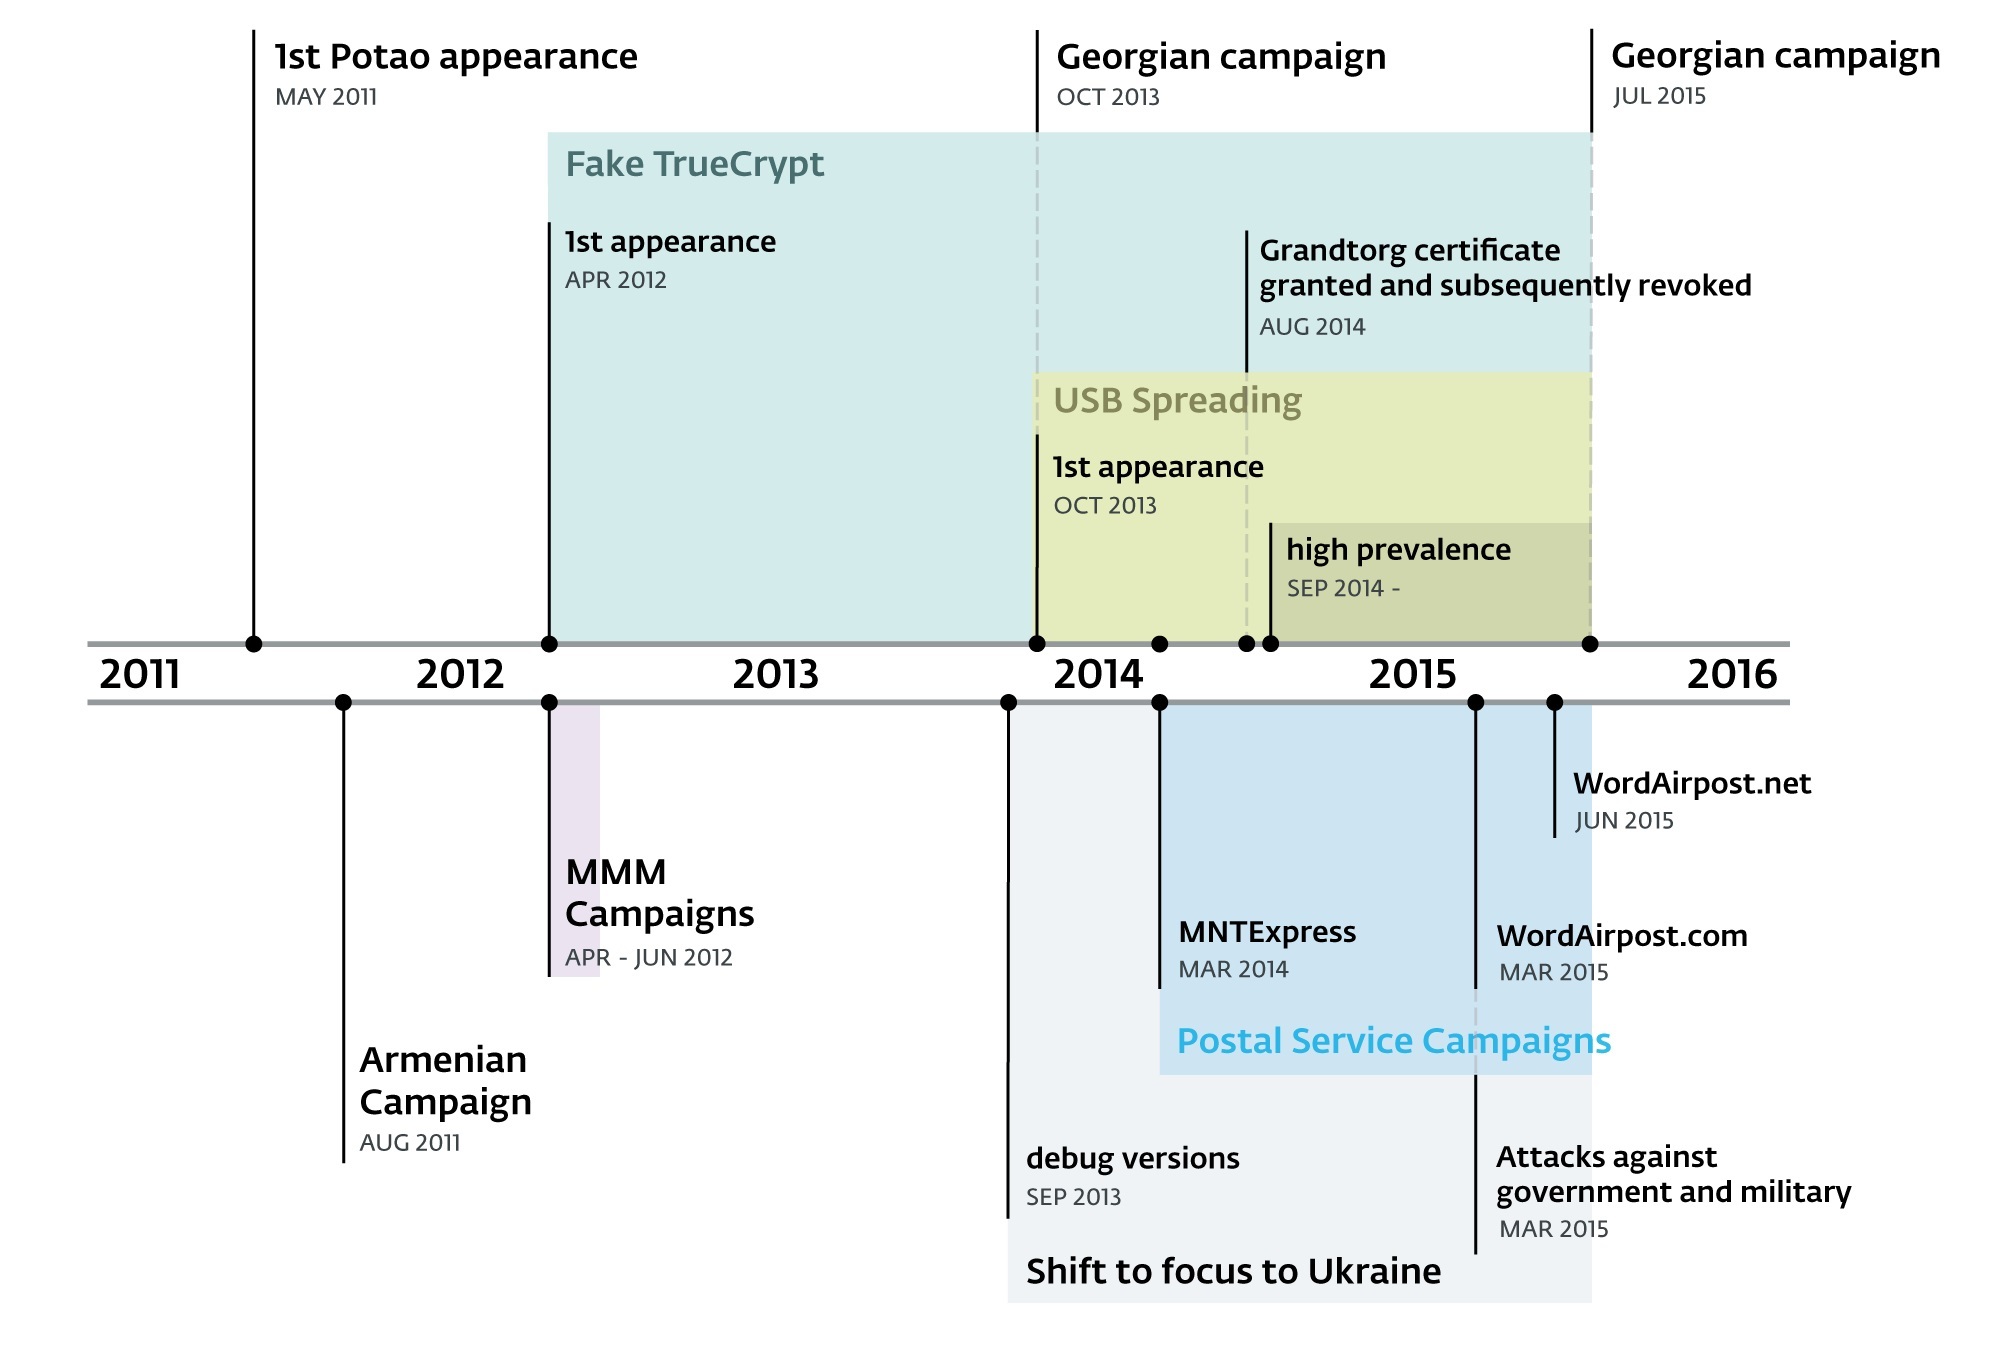
2011- July 2015
  • Aka  Sapotao and node69
  • Group - Sandworm / Quedagh APT
  • Vectors - USB, exe as doc, xls
  • Victims - RU, BY, AM, GE 
  • Victims - MMM group, UA gov
  • truecryptrussia.ru has been serving modified versions of the encryption software (Win32/FakeTC) that included a backdoor to selected targets. 
  • Win32/FakeTC - data theft from encrypted drives
  • The Potao main DLL only takes care of its core functionality; the actual spying functions are implemented in the form of downloadable modules. The plugins are downloaded each time the malware starts, since they aren't stored on the hard drive.
  • 1st Full Plugin and its export function is called Plug. Full plugins run continuously until the infected system is restarted
  • 2nd Light Plugin with an export function Scan. Light plugins terminate immediately after returning a buffer with the information they harvested off the victim's machine.
  • Some of the plugins were signed with a certificate issued to "Grandtorg":
  • Traffic 
  • Strong encryption. The data sent is encapsulated using the XML-RPC protocol.
  • MethodName value 10a7d030-1a61-11e3-beea-001c42e2a08b is always present in Potao traffic.
  • After receiving the request the C&C server generates an RSA-2048 public key and signs this generated key with another, static RSA-2048 private key .
  • In 2nd stage the malware generates a symmetric AES-256 key. This AES session key is encrypted with the newly received RSA-2048 public key and sent to the C&C server.
  • The actual data exchange after the key exchange is then encrypted using symmetric cryptography, which is faster, with the AES-256 key
  • The Potao malware sends an encrypted request to the server with computer ID, campaign ID, OS version, version of malware, computer name, current privileges, OS architecture (64 or 32bits) and also the name of the current process.
  • Potao USB - uses social engineering, exe in the root disguised as drive icon
  • Potao Anti RE -  uses the MurmurHash2 algorithm for computing the hashes of the API function names.
  • Potao Anti RE - encryption of strings
  • Russian TrueCrypt Win32/FakeTC - The malicious program code within the otherwise functional TrueCrypt software runs in its own thread. This thread, created at the end of the Mount function, enumerates files on the mounted encrypted drive, and if certain conditions are met, it connects to the C&C server, ready to execute commands from the attackers.
  • IOC https://github.com/eset/malware-ioc/tree/master/potao

TypeSHA256MD5
1stVersion1fe6af3d704d2fc0c7acd58b069a31eec866668ec6e25f52354e6e61266db8db85b0e3264820008a30f17ca19332fa19
1stVersion2ff0941fe3514abc12484ad2853d22fd7cb36469a313b5ecb6ef0c6391cf78abac854a3c91d52bfc09605506e76975ae
1stVersion54a76f5cd5a32ed7d5fa78e5d8311bafc0de57a475bc2fddc23ee4b3510b9d443b7d88a069631111d5585b1b10cccc86
1stVersion76c7c67274cf5384615a120e69be3af64cc31d9c4f05ff2031120612443c8360d1658b792dd1569abc27966083f59d44
1stVersion244c181eb442fefcf1e1daf900896bee6569481c0e885e3c63efeef86cd64c550c7183d761f15772b7e9c788be601d29
1stVersion887a721254486263f1f3f25f3c677da62ef5c062c3afa7ef70c895bc8b17b424a35e48909a49334a7ebb5448a78dcff9
1stVersion945c594aee1b5bd0f3a72abe8f5a3df74fc6ca686887db5e40fe859e3fc90bb1502f35002b1a95f1ae135baff6cff836
1stVersionab8d308fd59a8db8a130fcfdb6db56c4f7717877c465be98f71284bdfccdfa25a446ced5db1de877cf78f77741e2a804
1stVersionb22a614a291111398657cf8d1fa64fa50ed9c66c66a0b09d08c53972c6536766d939a05e1e3c9d7b6127d503c025dbc4
1stVersionfcfdcbdd60f105af1362cfeb3decbbbbe09d5fc82bde6ee8dfd846b2b844f97214634d446471b9e2f55158d9ac09d0b2
DebugVersion910f55e1c4e75696405e158e40b55238d767730c60119539b644ef3e6bc32a5d7263a328f0d47c76b4e103546b648484
DebugVersionc821cb34c86ec259af37c389a8f6cd635d98753576c675882c9896025a1abc53bdc9255df5385f534fea83b497c371c8
DebugVersionf845778c3f2e3272145621776a90f662ee9344e3ae550c76f65fd954e7277d195199fcd031987834ed3121fb316f4970
Droppersfrompostalsites4dcf14c41b31f8accf9683917bfc9159b9178d6fe36227195fabc232909452af65f494580c95e10541d1f377c0a7bd49
Droppersfrompostalsites8bc189dee0a71b3a8a1767e95cc726e13808ed7d2e9546a9d6b6843cea5eb3bda4b0615cb639607e6905437dd900c059
Droppersfrompostalsites048621ecf8f25133b2b09d512bb0fe15fc274ec7cb2ccc966aeb44d7a88beb5b07e99b2f572b84af5c4504c23f1653bb
Droppersfrompostalsitesaa23a93d2fed81daacb93ea7ad633426e04fcd063ff2ea6c0af5649c6cfa03851927a80cd45f0d27b1ae034c11ddedb0
Droppersfrompostalsitesc66955f667e9045ea5591ebf9b59246ad86227f174ea817d1398815a292b8c88579ad4a596602a10b7cf4659b6b6909d
Droppersfrompostalsitesd6f126ab387f1d856672c730991573385c5746c7c84738ab97b13c897063ff4ae64eb8b571f655b744c9154d8032caef
Dropperswdecoy61dd8b60ac35e91771d9ed4f337cd63e0aa6d0a0c5a17bb28cac59b3c21c24a9d755e52ba5658a639c778c22d1a906a3
Dropperswdecoy4328b06093a4ad01f828dc837053cb058fe00f3a7fd5cfb9d1ff7feb7ebb8e32b4d909077aa25f31386722e716a5305c
Dropperswdecoy15760f0979f2ba1b4d991f19e8b59fc1e61632fcc88755a4d147c0f5d47965c5fc4b285088413127b6d827656b9d0481
Dropperswdecoyb9c285f485421177e616a148410ddc5b02e43f0af375d3141b7e829f7d487bfd73e7ee83133a175b815059f1af79ab1b
Dropperswdecoycf3b0d8e9a7d0ad32351ade0c52de583b5ca2f72e5af4adbf638c81f4ad8fbcbeebbcb1ed5f5606aec296168dee39166
Dropperswdecoydbc1b98b1df1d9c2dc8a5635682ed44a91df6359264ed63370724afa9f19c7ee5a24a7370f35dbdbb81adf52e769a442
FakeTrueCryptextractedexe4c01ffcc90e6271374b34b252fefb5d6fffda29f6ad645a879a159f78e095979b64dbe5817b24d17a0404e9b2606ad96
FakeTrueCryptextractedexe5de8c04a77e37dc1860da490453085506f8aa378fbc7d811128694d8581b89ba7ca6101c2ae4838fbbd7ceb0b2354e43
FakeTrueCryptextractedexe73aae05fab96290cabbe4b0ec561d2f6d79da71834509c4b1f4b9ae714159b42f64704ed25f4c728af996eee3ee85411
FakeTrueCryptextractedexec7212d249b5eb7e2cea948a173ce96e1d2b8c44dcc2bb1d101dce64bb3f5beccc1f715ff0afc78af81d215d485cc235c
FakeTrueCryptSetup42028874fae37ad9dc89eb37149ecb1e6439869918309a07f056924c1b981deff34b77f7b2233ee6f727d59fb28f438a
FakeTrueCryptSetupa3a43bbc69e24c0bc3ab06fbf3ccc35cf8687e2862f86fb0d269258b68c710c9babd17701cbe876149dc07e68ec7ca4f
FakeTrueCryptSetupb8844e5b72971fe67d2905e77ddaa3366ae1c3bead92be6effd58691bc1ff8eccfc8901fe6a9a8299087bfc73ae8909e
FakeTrueCryptSetupfe3547f0e052c71f872bf09cdc1654137ee68f878fc6d5a78df16a13e6de176883f3ec97a95595ebe40a75e94c98a7bd
OtherDroppers2de76a3c07344ce322151dbb42febdff97ade8176466a3af07e5280bd859a18638e708fea8016520cb25d3cb933f2244
OtherDroppers4e88b8b121d768c611fe16ae1f008502b2191edc6f2ee84fef7b12b4d86fe000360df4c2f2b99052c07e08edbe15ab2c
OtherDroppers29dfc81b400a1400782623c618cb1d507f5d17bb13de44f123a333093648048f89a3ea3967745e04199ebf222494452e
OtherDroppers97afe4b12a9fed40ad20ab191ba0a577f5a46cbfb307e118a7ae69d04adc2e2d6ba88e8e74b12c914483c026ae92eb42
OtherDroppers793a8ce811f423dfde47a5f44ae50e19e7e41ad055e56c7345927eac951e966b043f99a875424ca0023a21739dba51ef
OtherDroppers904bb2efe661f654425e691b7748556e558a636d4f25c43af9d2d4dfbe83262e02d438df779affddaf02ca995c60cecb
OtherDroppersb62589ee5ba94d15edcf8613e3d57255dd7a12fce6d2dbd660fd7281ce6234f411b4e7ea6bae19a29343ae3ff3fb00ca
OtherDroppersd2c11706736fda2b178ac388206472fd8d050e0f13568c84b37683423acd155d27d74523b182ae630c4e5236897e11f3
OtherDroppersf1f61a0f9488be3925665f8063006f90fab1bf0bd0b6ff5f7799f8995ff8960e1ab8d45656e245aca4e59aa0519f6ba0
USBSpreaders1acae7c11fb559b81df5fc6d0df0fe502e87f674ca9f4aefc2d7d8f828ba7f5c76dda7ca15323fd658054e0550149b7b
USBSpreaders3d78f52fa0c08d8bf3d42074bf76ee56aa233fb9a6bc76119998d085d94368caca1a3618088f91b8fb2a30c9a9aa4aca
USBSpreaders7d15bd854c1dfef847cdd3caabdf4ab81f2410ee5c7f91d377cc72eb81135ff4a2bb01b764491dd61fa3a7ba5afc709c
USBSpreaders09c04206b57bb8582faffb37e4ebb6867a02492ffc08268bcbc717708d1a8919a59053cc3f66e72540634eb7895824ac
USBSpreaders12bb18fa9a12cb89dea3733b342940b80cd453886390079cb4c2ffcd664baeda2bd0d2b5ee4e93717ea71445b102e38e
USBSpreaders34e6fb074284e58ca80961feda4fe651d6d658077914a528a4a6efa91ecc749d057028e46ea797834da401e4db7c860a
USBSpreaders90b20b1687909c2f76f750ba3fd4b14731ce736c08c3a8608d28eae3f4cd68f3514423670de210f13092d6cb8916748e
USBSpreaders93accb71bf4e776955756c76990298decfebe4b1dd9fbf9d368e81dc1cb9532dabb9f4fab64dd7a03574abdd1076b5ea
USBSpreaders99a09ad92cc1a2564f3051057383cb6268893bc4a62903eabf3538c6bfb3aa9c542b00f903f945ad3a9291cb0af73446
USBSpreaders339a5199e6d0b5f781b08b2ca0ad0495e75e52b8e2fd69e1d970388fbca7a0d6a427ff7abb17af6cf5fb70c49e9bf4e1
USBSpreaders340b09d661a6ac45af53c348a5c1846ad6323d34311e66454e46c1d38d53af8b2646f7159e1723f089d63e08c8bfaffb
USBSpreaders461dd5a58ffcad9fffba9181e234f2e0149c8b8ba28c7ea53753c74fdfa0b0d5609abb2a86c324bbb9ba1e253595e573
USBSpreaders4688afcc161603bfa1c997b6d71b9618be96f9ff980e5486c451b1cc2c5076cbae552fc43f1ba8684655d8bf8c6af869
USBSpreaders7492e84a30e890ebe3ca5140ad547965cc8c43f0a02f66be153b038a73ee53141234bf4f0f5debc800d85c1bd2255671
USBSpreaders61862a55dcf8212ce9dd4a8f0c92447a6c7093681c592eb937a247e38c8109d4e685ea8b37f707f3706d7281b8f6816a
USBSpreaders95631685006ac92b7eb0755274e2a36a3c9058cf462dd46f9f4f66e8d67b9db29179f4683ece450c1ac7a819b32bdb6d
USBSpreadersb8b02cc57e45bcf500b433806e6a4f8af7f0ac0c5fc9adfd11820eebf4eb5d79cdc60eb93b594fb5e7e5895e2b441240
USBSpreaderse57eb9f7fdf3f0e90b1755d947f1fe7bb65e67308f1f4a8c25bc2946512934b739b67cc6dae5214328022c44f28ced8b
USBSpreaderse3892d2d9f87ea848477529458d025898b24a6802eb4df13e96b0314334635d03813b848162261cc5982dd64c741b450
USBSpreadersf1d7e36af4c30bf3d680c87bbc4430de282d00323bf8ae9e17b04862af28673635724e234f6258e601257fb219db9079


Read more
  1. Hacking Web Sql Injection Pdf
  2. Hacking Usb
  3. Hacking Course
  4. Hacker Etico
  5. Python Hacking
  6. Quiero Ser Hacker
  7. Hackers Informaticos Contactar

How To Switch From 32-Bit Windows 10 To 64-Bit Windows 10

Microsoft offers Windows 10 as a free upgrade for computers running a genuine copy of Windows 7 or Windows 8.1. Also, similar to previous releases, the operating system is available on different editions and two versions: 32-bit and 64-bit.While upgrading from Windows 10 Home to Windows 10 Pro is not free, what many people are unfamiliar with is that Microsoft won't ask for more money to upgrade from a 32-bit to a 64-bit version.
However, the upgrade path only allows moving from a qualifying version to its equivalent edition on the same architecture. This limit means that if your PC is running a 32-bit version of Windows 8.1, after the upgrade you'll be stuck with the 32-bit version of Windows 10 — even if your computer's processor can handle the 64-bit version. The only solution is to make a clean installation of the operating system and reconfigure all your apps and settings.
iemhacker-how-to-switch-from-32-bit-windows-to 64bit
In this Windows 10 guide, we'll walk you through the steps to verify whether your computer in fact includes support for a 64-bit version and we'll guide you through the upgrade process to Windows 10 (x64).

Make sure Windows 10 64-bit is compatible with your PC

A 64-bit version of Windows can only be installed on computers with capable hardware. As such, the first thing you need to do is to determine whether your computer has a 64-bit processor.
You can easily get this information from the Settings app.
  1. Use the Windows key + I keyboard shortcut to open the Settings app.
  2. Click System.
  3. Click About.
  4. Under System type, you will see two pieces of information: if it says 32-bit operating system, x64-based processor, then it means that your PC is running a 32-bit version of Windows 10 on a 64-bit processor. If it says 32-bit operating system, x86-based processor, then your computer doesn't support Windows 10 (64-bit).

Make Sure Your Processor is 64-bit Capable

First thing's first. Before even thinking of upgrading to 64-bit Windows, you'll need to confirm that the CPU in your computer is 64-bit capable. To do so, head to Settings > System > About. On the right-hand side of the window, look for the "System type" entry.

You'll see one of three things here:

  • 64-bit operating system, x64-based processor. Your CPU does support 64-bit and you already have the 64-bit version of Windows installed.
  • 32-bit operating system, x86-based processor. Your CPU does not support 64-bit and you have the 32-bit version of Windows installed.
  • 32-bit operating system, x64-based processor. Your CPU supports 64-bit, but you have the 32-bit version of Windows installed.
If you see the first entry on your system, you don't really need this article. If you see the second entry, you won't be able to install the 64-bit version of Windows on your system at all. But if you see the last entry on your system—"32-bit operating system, x64-based processor"—then you're in luck. This means you're using a 32-bit version of Windows 10 but your CPU can run a 64-bit version, so if you see it, it's time to move on to the next section.
Make Sure Your PC's Hardware Has 64-bit Drivers Available
Even if your processor is 64-bit compatible, you might want to consider whether your computer's hardware will work properly with a 64-bit version of Windows. 64-bit versions of Windows require 64-bit hardware drivers, and the 32-bit versions you're using on your current Windows 10 system won't work.
Modern hardware should certainly offer 64-bit drivers, but very old hardware may no longer be supported and the manufacturer may have never offered 64-bit drivers. To check for this, you can visit the manufacturer's driver download web pages for your hardware and see if 64-bit drivers are available. You shouldn't necessarily need to download these from the manufacturer's website, though. They are likely included with Windows 10 or automatically will be downloaded from Windows Update. But old hardware—for example, a particularly ancient printer—simply may not offer 64-bit drivers.

Upgrade by Performing a Clean Install

You'll need to perform a clean install to get to the 64-bit version of Windows 10 from the 32-bit one. Unfortunately, there's no direct upgrade path.
Warning: Back up your important files before continuing and also make sure you have what you need to reinstall your programs. This process will wipe your whole hard disk, including Windows, installed programs, and personal files.
First, if you haven't upgraded to Windows 10 yet, you'll need to use the upgrade tool to upgrade. You'll get the 32-bit version of Windows 10 if you were previously using a 32-bit version of Windows 7 or 8.1. But the upgrade process will give your PC a Windows 10 license. After upgrading, be sure to check that your current 32-bit version of Windows 10 is activated under Settings > Update & security > Activation.
Once you're using an activated version of the 32-bit Windows 10, download the Windows 10 media creation tool from Microsoft. If you're using the 32-bit version of Windows 10 at the moment, you'll have to download and run the 32-bit tool.
When you run the tool, select "Create installation media for another PC" and use the tool to create a USB drive or burn a disc with Windows 10. As you click through the wizard, you'll be asked whether you want to create 32-bit or 64-bit installation media. Select the "64-bit (x64)" architecture.
Next, restart your computer (you did back everything up, right?) and boot from the installation media. Install the 64-bit Windows 10, selecting "Custom install" and overwriting your current version of Windows. When you're asked to insert a product key, skip the process and continue. You'll have to skip two of these prompts in total. After you reach the desktop, Windows 10 will automatically check in with Microsoft and activate itself. You'll now be running the 64-bit edition of Windows on your PC.
If you want to go back to the 32-bit version of Windows, you'll need to download the media creation tool—the 64-bit version, if you're running the 64-bit version of Windows 10—and use it to create 32-bit installation media. Boot from that installation media and do another clean install—this time installing the 32-bit version over the 64-bit version.

Final Words :

Finally, you are aware of the way through which you could be able to switch from the 32-bit windows to 64-bit windows really easily. There will be no difference in the functions or the working of the windows yet the only change that you will get is the more advanced architecture that is compatible with numerous high-end apps. If you are thinking to switch your windows to the 64-bit version then make sure you first check for your hardware compatibility. Hopefully, you would have liked the information of this post, please share this post with others if you really liked it. Provide us your valuable views regarding this post through using the comments section below. At last nevertheless thanks for reading this post!
Related links

May 19, 2020

Entropy: Netwave And GoAhead IP Webcams Exploiting Tool


About Entropy Toolkit
   Entropy Toolkit is:
  • A set of tools to exploit Netwave and GoAhead IP Webcams.
  • A powerful toolkit for webcams penetration testing.

Entropy Toolkit's installationEntropy Toolkit's execution

Entropy Toolkit's examples:
  • Example of exploiting a single webcam
    entropy -b 1 -i [webcam's ip address and port] -v
    Example: entropy -b 1 -i 192.168.1.100:80 -v
  • Example of exploiting webcams from a list
    entropy -b 2 -l [file text] -v
    Example: entropy -b 2 -l iplist.txt -v
  • Example of exploiting webcams using shodan
    entropy -b 2 -v --shodan [you shodan api key]
    Example: entropy -b 2 -v --shodan PSKINdQe1GyxGgecYz2191H2JoS9qvgD

Entropy Toolkit disclaimer:
   Usage of the Entropy Toolkit for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state, federal, and international laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program.

Entropy Toolkit license: MIT license.

Download Entropy Toolkit
(Sign up Windscribe for free, get full protection and stay anonymous
with the best free VPN. Read more here)
More info
  1. Paginas Para Hackear
  2. Hacking Team
  3. Hacking Social
  4. Codigo Hacker
  5. Paginas Para Hackear
  6. Whatsapp Hacking
  7. Libros De Hacking Pdf

BurpSuite Introduction & Installation


What is BurpSuite?
Burp Suite is a Java based Web Penetration Testing framework. It has become an industry standard suite of tools used by information security professionals. Burp Suite helps you identify vulnerabilities and verify attack vectors that are affecting web applications. Because of its popularity and breadth as well as depth of features, we have created this useful page as a collection of Burp Suite knowledge and information.

In its simplest form, Burp Suite can be classified as an Interception Proxy. While browsing their target application, a penetration tester can configure their internet browser to route traffic through the Burp Suite proxy server. Burp Suite then acts as a (sort of) Man In The Middle by capturing and analyzing each request to and from the target web application so that they can be analyzed.


Everyone has their favorite security tools, but when it comes to mobile and web applications I've always found myself looking BurpSuite . It always seems to have everything I need and for folks just getting started with web application testing it can be a challenge putting all of the pieces together. I'm just going to go through the installation to paint a good picture of how to get it up quickly.

BurpSuite is freely available with everything you need to get started and when you're ready to cut the leash, the professional version has some handy tools that can make the whole process a little bit easier. I'll also go through how to install FoxyProxy which makes it much easier to change your proxy setup, but we'll get into that a little later.

Requirements and assumptions:

Mozilla Firefox 3.1 or Later Knowledge of Firefox Add-ons and installation The Java Runtime Environment installed

Download BurpSuite from http://portswigger.net/burp/download.htmland make a note of where you save it.

on for Firefox from   https://addons.mozilla.org/en-US/firefox/addon/foxyproxy-standard/


If this is your first time running the JAR file, it may take a minute or two to load, so be patient and wait.


Video for setup and installation.


You need to install compatible version of java , So that you can run BurpSuite.

Related word


  1. Hacking Code
  2. Hacking To The Gate
  3. Hacking Hardware Tools
  4. Hacking Wifi Android
  5. Reddit Hacking
  6. Que Estudiar Para Ser Hacker
  7. Hacking Tor Whatsapp

How To Hack Any Whatsapp Account In 2020

The article will also be broken down into different subtopics and subcategories. This to make it easy for those who are just interested in skimming through the article to pick the part of WhatsApp hack they are most interested in. Just incase you don't have enough time to go through the entire article.

Search queries like these are a common place; Can WhatsApp be hacked? Can you read WhatsApp messages? How safe is the most popular trade fair in the world? This article gives you all the solution you need to hack any WhatsApp account, as well as how to protect yourself from a WhatsApp hack attack.

Although the messenger is now on an end-to-end encryption, WhatsApp is still not totally safe from espionage. WhatsApp chats and messages can still be accessed and read remotely, and old &deleted WhatsApp chats and messages retrieved.

WhatsApp Spy: Hack WhatsApp Chats and Messages

A very simple solution is to use a software that can hack WhatsApp remotely. All manufacturers offer to read the WhatsApp messages an extra web portal. In addition to the Whatsapp messages but can also spy on other messengers. So you can also have access to social media accounts.

The software may only be installed on a smartphone. If the user of the smartphone has been informed about the installation and effects.

WhatsApp Hacker: 3 Steps to Hack WhatsApp in 2020

You can hack Whatsapp using a second cell phone. No extra SIM card is necessary for this. The guide also works with a tablet. With this method, the other phone only needs to clone WhatsApp messages is internet connection.

The trick to hack Whatsapp successfully is not a software bug. It's the way WhatsApp has developed the setup wizard. Since there are no user accounts with passwords and you log in via the mobile number, here lies the vulnerability. But you can also protect yourself from the Whatsapp hack.

Hack WhatsApp Chat with the Best WhatsApp Hacking Tool

To read Whatsapp messages, the mobile phone number of the target must be known. The cell phone can remain locked. There is no need to install software to hack and read Whatsapp messages. Even with the PIN or fingerprint, the Whatsapp account can be hacked.

STEP 1: Create a New WhatsApp Account

To hack an account from Whatsapp, the app from the App Store must be installed on the second cell phone. After the installation of Whatsapp, target's phone number is entered. A confirmation request must be waited until access to the smartphone of the victim exists.

STEP 2: WhatsApp Account Confirmation

The confirmation of the Whatsapp account is the actual security risk of the messenger. Whatsapp usually confirms the registration via SMS. Occasionally the confirmation will also be sent by automated phone call via a phone call.

Calls and text messages can be read and taken by anyone even when the screen is locked. So that the WhatsApp hack does not stand out, the SMS must be removed from the start screen by swiping.

STEP 3: Enter Confirmation

The stolen verification PIN is now entered on the second smartphone. As a result, the WhatsApp account has been taken over by you. You can read the WhatsApp messages, which respond to this mobile phone number.

The downside to this trick is that the victim immediately notices the Whatsapp hack as soon as Whatsapp is opened. If the victim goes through the sign-in process again. The attacker loses access to the messages and no Whatsapp messages can be read.

How to Hack Someone's WhatsApp in 2020

A good way to hack a WhatsApp account is to hack whatsapp online. Here you can read WhatsApp messages via a browser and also write. The target user can continue to use his cell phone (works for iOS, Android phone etc) and does not notice the WhatsApp hack.

STEP 1: Access the Cell Phone

In order to be able to read WhatsApp messages by installing software. Access to the unlocked smartphone is required for a short time. In addition, cell phone, a computer or laptop is necessary. On this the Whatsapp messages will be read later.

STEP 2: Access WhatsApp Web

If you have access to the unlocked smartphone, Whatsapp must be started there. The Whatsapp settings include Whatsapp Web . If this is selected, Whatsapp opens a QR code scanner with the hint to open WhatsApp Web in the browser.

If the QR code is scanned in the browser with the smartphone. There is a permanent connection and Whatsapp messages can be read. If you want to hack Whatsapp in this way. You have full access to all incoming messages and you can even write messages yourself.

STEP 3: Read WhatsApp Messages

The target usually sees this Whatsapp hack only when the settings are invoked to Whatsapp Web in the app. Whatsapp messages can be read via the browser. Regardless of whether the smartphone is on home Wi-Fi or on the move. You can also hack group chats admin by just having any of the contact details.

WhatsApp Hack: How to Hack any WhatsApp account

Which is the most popular messaging app globally? Of course, you can use different apps from Android or iOS to send and receive messages. But Whatsapp remains everyone's favorite globally!

Whatsapp is one of the popular apps in the world. There are more than 2 billion active users on Whatsapp, messaging daily with the app. Why do people love WhatsApp? Whatsapp is very convenient and easy to use.

Other messaging apps like Facebook Messenger, still needs a special account to sign up for this app. If you change a new app, you'll need to add another account. This can be stressful, as you have to remember a lot of new passwords and usernames.

HACKER NT

More info


Social Engineering Pentest Professional(SEPP) Training Review

Intro:
I recently returned from the new Social Engineering training provided by Social-Engineer.org in the beautiful city of Seattle,WA, a state known for sparkly vampires, music and coffee shop culture.  As many of you reading this article, i also read the authors definitive book Social Engineering- The art of human hacking and routinely perform SE engagements for my clients. When i heard that the author of the aforementioned book was providing training i immediately signed up to get an in person glance at the content provided in the book. However, i was pleasantly surprised to find the course covered so much more then what was presented in the book.

Instructors:


I wasn't aware that there would be more then one instructor and was extremely happy with the content provided by both instructors. Chris and Robin both have a vast amount of knowledge and experience in the realm of social engineering.  Each instructor brought a different angle and use case scenario to the course content. Robin is an FBI agent in charge of behavioral analysis and uses social engineering in his daily life and work to get the results needed to keep our country safe. Chris uses social engineering in his daily work to help keep his clients secure and provides all sorts of free learning material to the information security community through podcasts and online frameworks.


Course Material and Expectation: 
I originally thought that the material covered in class would be a live reiteration of the material covered in Chris's book. However, I couldn't have been more wrong !!  The whole first day was about reading yourself and other people, much of the material was what Robin uses to train FBI agents in eliciting information from possible terrorist threats. Each learning module was based on live demo's, nightly labs, and constant classroom interaction. Each module was in depth and the level of interaction between students was extremely useful and friendly. I would say the instructors had as much fun as the students learning and sharing social techniques and war stories.
The class was heavily made up of ways to elicit personal and confidential information in a way that left the individuatial "Happier for having met you".  Using language, body posture and social truisms as your weapon to gather information, not intended for your ears, but happily leaving the tongue of your target.
Other class activities and materials included an in depth look at micro expressions with labs and free extended learning material going beyond the allotted classroom days.  Also break out sessions which focused on creating Phone and Phishing scripts to effectively raise your rate of success. These sessions were invaluable at learning to use proper language techniques on the phone and in email to obtain your objectives.

Nightly Missions/Labs: 
If you think that you are going to relax at night with a beer. Think again!! You must ensure that your nights are free, as you will be going on missions to gain information from live targets at venues of your choice.  Each night you will have a partner and a mission to gain certain information while making that persons day better then it started.  The information  you are requested to obtain will change each night and if done properly you will notice all of the material in class starting to unfold.. When you get to body language training you will notice which targets are open and when its best to go in for the kill. You will see interactions change based on a persons change in posture and facial expressions. Each day you will take the new techniques you have learned and put them into practice. Each morning you have to report your findings to the class..
During my nightly labs i obtained information such as door codes to secured research facilities, information regarding secret yet to be released projects.  On the lighter side of things i obtained much personal information from my targets along with phone numbers and invitations for further hangouts and events. I made many new friends inside and outside of class.
There were also labs within the confines of the classroom such as games used to solidify your knowledge and tests to figure out what kind of learner you are. Technical labs on the use of information gathering tools and ways to use phone and phishing techniques to your advantage via linguistically and technologically. Essentially the class was about 60% interaction and labs.


Proof it works:
After class i immediately had a phishing and phone based contract at my current employment. I used the email and phone scripts that we created in class with 100% click rate and 100% success in phone elicitation techniques. Gaining full unfettered access to networks through phone and email elicitation and interaction. Although I do generally have a decent SE success rate, my rates on return are now much higher and an understanding of what works and what doesn't, and why are much more refined.


Conclusion and Certification:
I paid for this class out of pocket, including all expenses, hotels, rentals cars and planes etc etc. I would say that the class was worth every penny in which i paid for it. Many extras were given including black hat passes, extended training from notable sources and continued interaction from instructors after class ended. I would highly recommend this class to anyone looking for a solid foundation in social engineering or a non technical alternative to training.  You will learn a lot, push yourself in new ways and have a blast doing it. However I did not see any sparkly vampires while in seattle.... Twilight lied to me LOL
The certification is a 48 hour test in which you will utilize your knowledge gained technologically and socially to breach a company.I am not going to give away to much information about the certification as i haven't taken it yet and I do not want to misspeak on the subject. However I will say that social-engineer.org has done an excellent job at figuring out a way to include Real World Social Engineering into a test with verifiable proof of results. I am going to take my test in a couple weeks and it should be a blast!!!

Thanks and I hope this review is helpful to all those looking for SE training.  I had a blast :) :)

Related word


  1. El Hacker Pelicula
  2. Cracker Informatico
  3. Hacking Online Games
  4. Hacking To The Gate Lyrics
  5. Drupal Hacking
  6. Curso De Hacking
  7. Libros De Hacking Pdf
  8. Hacking Wifi Kali Linux
  9. Curso De Hacking Gratis
  10. Programa Hacker
  11. Programas Para Hackear
  12. House Hacking
  13. Como Empezar A Hackear
  14. Tecnicas De Ingenieria Social

May 18, 2020

DOWNLOAD XSSTRIKE – ADVANCED XSS EXPLOITATION SUITE

XSSTRIKE – ADVANCED XSS EXPLOITATION SUITE

XSStrike is really advanced XSS exploitation and detection suite, which contains a very powerful XSS fuzzer and provides no false positive results using fuzzy matching. XSStrike is the first XSS scanner that generates its own payloads. Download xsstrike and test it out.
It also has built in an artificial intelligent enough to detect and break out of various contexts.

FEATURES:

  • Powerful Fuzzing Engine
  • Context Breaking Intelligence
  • AI Payload Generation
  • GET & POST Methods Support
  • Cookie Support
  • WAF Fingerprinting
  • Handcrafted Payloads to Filter and WAF Evasion
  • Hidden Parameter Discovery
  • Accurate Results

DOWNLOAD XSSTRIKE – ADVANCED XSS EXPLOITATION SUITE

Click here to download xsstrike.
More information
  1. Penetration Testing A Hands-On Introduction To Hacking
  2. Growth Hacking Instagram
  3. Que Estudiar Para Ser Hacker
  4. Hacking In Spanish
  5. Hacking Microsoft
  6. Travel Hacking
  7. Hacking Udemy
  8. Hacking Smart Tv
  9. Hacking Websites
  10. Clases De Hacker
  11. Crack Definicion